Off the Radar: How Unapproved AI Is Complicating Healthcare Cyber Risk
You cannot secure what you cannot see, and right now, healthcare organizations are accumulating hidden cyber liabilities with every keystroke.
You cannot secure what you cannot see, and right now, healthcare organizations are accumulating hidden cyber liabilities with every keystroke.
We’re entering uncharted territory if bad actors can both launch zero-days and exploit unaddressed backdoors with new efficiency. This is why teams need to unify their network structure and better forecast what they’re up against.
We have the opportunity to design systems that give people greater capacity for the work where human presence matters most: listening, understanding, reassuring, deciding, and caring.
The adversaries targeting critical infrastructure today are not always chasing a ransom. Sometimes, they are chasing chaos. That distinction matters, and most healthcare organizations are not yet prepared for it.
Building a medical practice that’s truly resilient can feel like pushing a rock up a hill. However, physicians who are ready, willing and able to stay adaptable and seize opportunities will give their medical practices staying power.
Now is the time to solve the industry’s identity crisis, and it can only be done through a combination of phishing-resistant and adaptive MFA, fine-grained access control, and standards-based interoperability.
As legal and compliance professionals, we champion privacy and cybersecurity in our organizations — but success requires a team effort.
Healthcare decision-makers, especially at pharmaceutical companies, must prioritize patient input. Data collected from social media listening is a significant step in the right direction.
The core challenge for leadership is no longer merely managing direct vendors; it’s the cascading risk of the "nth-party" supplier.
We’re losing the patching battle and therefore the ransomware war. Here's how healthcare can change its perspective, improve patching, and better block ransomware pathways.
This new standard was developed to address the rise of telehealth, cybersecurity risks/compliance in ePrescribing, data needs, AI, and the growing demand for patient transparency. So what is the Standard solving for, and what can providers expect?
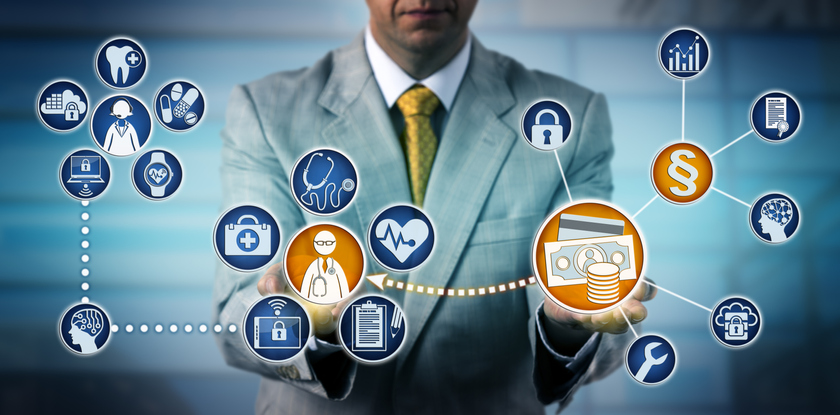
Simplifying payments isn’t just about transactions; it’s about building better relationships and ensuring financial health through protection, payment choice, scale, and integration.
What if health plans could identify member decline before an avoidable hospitalization occurs? Real-time clinical visibility into long-stay SNF members uncovers risk earlier and drives better outcomes.
The MedTech industry has demonstrated remarkable resilience in navigating uncertainty, and 2025 promises to be a pivotal year as the election supercycle concludes and AI regulatory frameworks become clearer.
Recognizing its vulnerability to cybercrime, the healthcare industry continues to prioritize cybersecurity. Here are some areas where organizations should be focusing their efforts.
Technology often plays a critical role in strategies to combat rising costs while maintaining quality care. Here are four trends expected to accelerate in 2025.
To protect healthcare organizations and minimize the risk of breaches, software development companies must stay vigilant regarding the biggest vulnerability of any digital system: the users. Here are some ways to minimize irresponsible digital behavior and some tools to enhance the security of medical digital systems.
It has become standard practice for healthcare organizations to focus on identifying and stopping external threats to the privacy and security of data, but one often overlooked risk may be right inside your offices — snooping employees and malicious insider threats.